HSMAttest / Features
Features
This page is still under development.
Features
Core Secrets protected by HSM - limited use secrets provided to attested workloads - explicitly governed access.
- HSM-protected master secrets: core secrets remain within the HSM protection boundary.
- Attestation-gated access: workloads demonstrate their identity and state before obtaining access.
- Governance: explicitly allowed actors and actions protect the HSM core and its contents. There is a complete and auditable Chain of Governance from initial Setup to current state.
- HSM access by whitelists: no enrollment by correct Governance -> no access.
- Derived keys: workloads use short-lived or limited-scope keys rather than master secrets.
- Confidential Computing integration: approved workloads handle sensitive operations inside protected execution environments.
- Choice of Confidential Computing technology and framework is pluggable.
- Operational tooling and practices: support for deployment, HSM operations and secure software supply-chain integration.
- High Availability and large-scaling supported by External HSM Storage.
- Support for SIEM and Performance Monitoring.
Delivery choices
- Self-developed deployments with SDK
- OEM and White Label Repackaging
- Preconfigured, customisable Managed Services
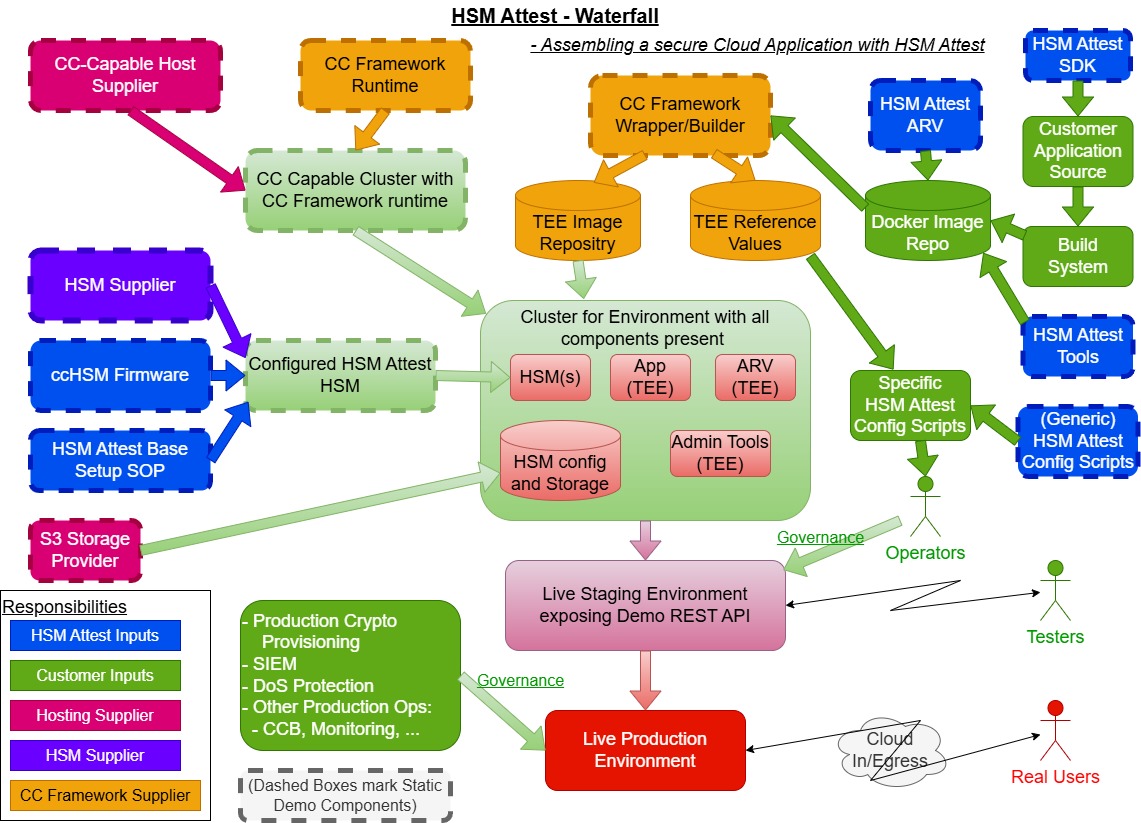
The diagram below shows how the different components of a system running with HSMAttest fit together and how they could be divided up according to different providers.